The Arson Warehouse link leads to webpage which asks for installation of some suspicious file, I don't think the link would be safe anymore. Furthermore, the "Travel Planning Sites and Guides" which are being talked about no longer exist. This is a good guide, however, it requires revision.
Well, you DO select all the items through the checkbox- though I agree we're in a grey area. Manual selection happens together at the beginning, and then one sell button works for all the "selected" items. I think the one action, one interaction rule would be intended for disallowing some kind of "farming" or making API calls in the background.
I'm trying to get into contact with the staff, let's see what they have to say about it. Anyway, thanks for pointing it out! Have a great day!
I found this while searching for TORN's scripting rules:
"If the software you're using makes non-API requests that are not manually triggered by you, it is not allowed and can be tracked."
I see that each server-side action is being triggered by one deliberate human action, it isn't automated in a loop without per-action human input, right? I would say it's a grey area, not a complete breach.
I think that's what you meant, because .click() in JS is standard for scripting. Anyway, can you suggest how to verify the script for compliance?
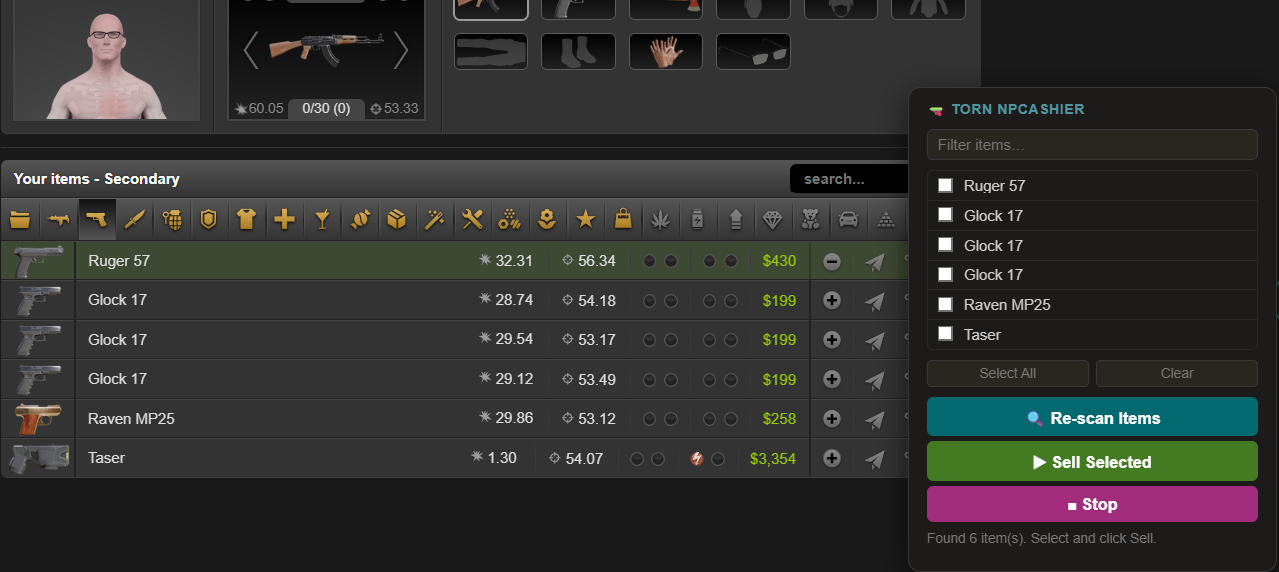
This is how it looks as of now. And yes, it works. Sometimes the refresh rate is slow and you might see that the items are not sold but that's not the case (visual glitch). Since it's client-side active, it'll show that it "skipped" the item, but you can simply refresh the page and see that the item was indeed sold.