Skip to content
TORNLIFE More

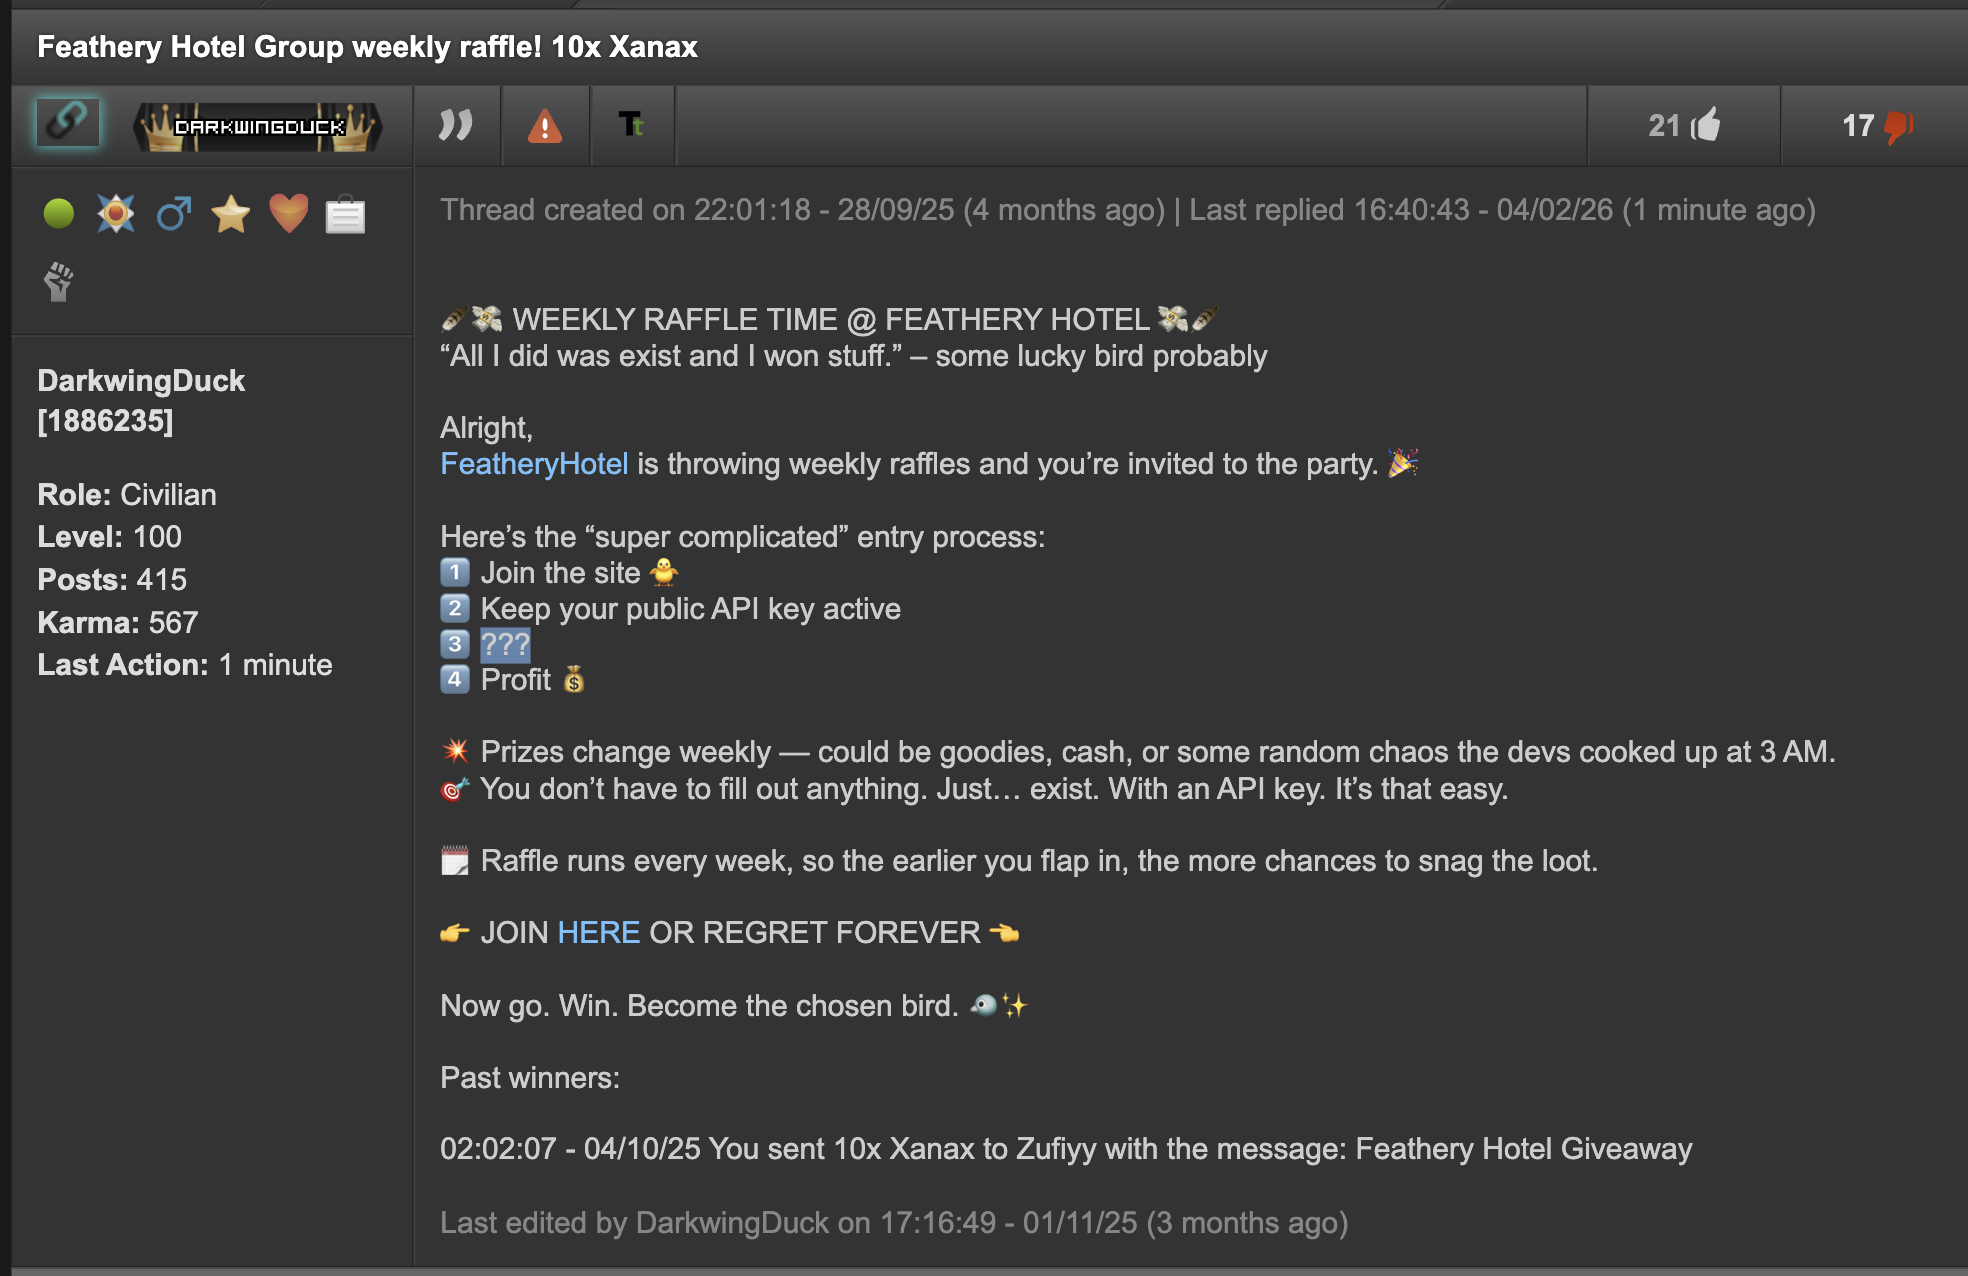
Feathery Hotel Group weekly raffle! 10x Xanax

Started by DarkwingDuck [1886235] on in Fun & Games.

189 replies · 1.12k views · thread synced · 4 days ago · View on torn.com

Posts archived: 190 / 190 posts (100%) · the total is Torn's reply count + the opening post at the last fetch

DarkwingDuck [1886235]

The terms of service are there for anyone to view and plainly says what all we will and will not use api keys for. 

 Also, in the steps you're forgetting the ??? Step this eludes to things going on you're unaware of. If the key is still submitted, they are comfortable with their level of understanding 


None of the key providers have been mugged because of, or, in connection to our API collection.


Raffles happen every week with occasional special raffle


Legendary, I understand your frustration but after having checked with staff prior to posting this thread this is borderline harassment.


Try to self hosp before your sell all your stuff. 

LegendaryKing11 [2804919]

Are you serious? Harassment? Just speaking facts on you not making your ToS transparent and disguise this forum thread as a plain giveaway thread with no catch. 


What do you mean the "???" steps elude to things I am unaware of? Should you clarify what happens to this step then? Please do a full disclosure on what this does. Most noobs I have messaged have come back to me and mentioned they're unaware of you using their keys in a mug bot so you definitely do not do a good job disclosing what you are doing.


I don't even understand why this post is in F&G, shoudln't it be in Trading Post instead? There's no games here except the business transaction of noobs selling you API keys for your mugging purposes. 


You know what you're doing. Admit it. 


ScroogeMcDuck [115716] Reporter

Chiming in here -- not sure what the "gotcha" is here. We don't use their personal data, events, logs, etc. We use their API key with their consent as a public key to look at other player's bazaar sales, not their personal data.

They have absolute control of their API key, as your messages point out, to disable their key either through our interface or through Torn's API panel. We also comment on any API calls for transparency.

I'm aware you don't like mug bots from your constant posts about how much you don't like mug bots.

The likelihood that we're going to mug one of these players is low (again, we're not using their keys for their events or data). The likelihood that we're going to give them almost $10m in a given week is high. We've given away close to $200m in prizes in the last few months.

DarkwingDuck [1886235]

AI Overview


+5

Yes, a raffle is considered a game of chance and a form of gambling in the United States, defined by participants purchasing tickets for a chance to win a prize through a random drawing. 

DarkwingDuck [1886235]

Did you read the terms of service? It's blatantly obvious. 

ToS is there for a reason. 


Stop derailing our happy raffle thread. 


You've said your 2 cents

LegendaryKing11 [2804919]

Change the "???" to "We will use your API key to mug people" for full transparency. Have a problem? 

Or spend time to click into your website and then click into your ToS and read your word salad about "Discord notifications about players holding large amounts of cash after events such as selling items through Item Market/Bazzar"


This is just shady af.

DarkwingDuck [1886235]

ToS 1st sentence:  By submitting your API key, you are allowing your key to be used by a bot for the purposes of cross-referencing datapoints amongst users to gain insights to when users are holding large amounts of cash with the intention of mugging them

DarkwingDuck [1886235]

No we don't treat everyone like they have an inability to read.

We've done what's required and been transparent and open about it with anyone who has read or asked directly.

Unlucky [2472585]

This seems like such an odd interaction. 

If you think you’re being transparent and doing nothing wrong in your bot you could just add in the OP to this post that the users APIs will be used to power a mug bot. 

Seems your target audience is noobs who want free stuff and won’t really know what the api is doing so why not just be honest in your post and save yourself the drama 

Abetting [2016807]

If you weren't trying to be shady you would simply disclose the true purpose on the description not need to be read on the ToS.


You don't want to do a raffle, you want API keys to feed mug bots. State your intentions clearly or at least stop playing dumb like you didn't intentionally hide the true purpose behind a tos you know half or more people won't read.


Why does the primary post here not mention a single thing about it if you care about transparency? Transparency isn't waiting for someone to ask questions, it's leaving everything out for all to see so they don't need to.


Tentacles [3163623]

Are you aware that when the new policies about needing clearer disclosure on what you are using collected api keys for were created, the whole debate that sparked them was over a tool using public key information (eg. not that user's personal information). The old bazaar aggregator as it happens. And staff's stance at the time was that regardless of it being public information every particular usecase needed to be made very clear to the key owner.


When creating a script, userscript, sheet, extension, API service, bot, 3rd party website or any other API tool (collectively "service"), the end user must be aware of how will their API key be used.


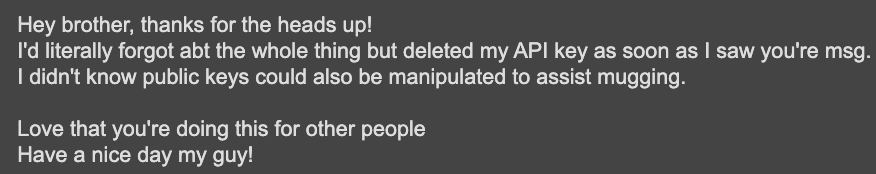
This is their obligation. According to torn. You think the noobs they are requesting keys from are too dumb to read and understand? Then perhaps they shouldn't be using their keys. (But they clearly can read and understand, as you can see by them responding when someone acutally messaged them to let them know what their keys were being used for.)


Every f***ing legitimate tool out there has moved towards having better disclosure, even when their services are purely in the interest of the key owners, even when this extra bureaucracy can get annoying as hell, yet here you are being as sneaky as you possibly can get away with for something that even with proper disclosure would pretty much put you on the same level as scamming noobs for losses.


This kind of utter bullshit is exactly why the acceptable use guidelines were needed and created. I would be surprised if this thread is allowed to continue in its current format, but if it is, that pretty much means those guidelines are pointless, and have failed at the one useful thing they were designed to accomplish.


While we are on the topic, I would fully support someone making a suggestion that collecting api keys from users in exchange for benefits unrelated to what the keys are being used for, and/or using keys for purposes that don't directly or indirectly benefit the key owner, should simply not be allowed. (Yes, I'm aware that would also harm some benign and useful data collection projects, I think that's an acceptable tradeoff.)

Apatxe [2813453]

Not really... The new guidelines state: 


If the service is not storing or sharing the data or the key anywhere, it's enough to state so, otherwise ToS with the information above needs to be clearly and visibly stated in any place where user is providing their API key in the table format highlighted above.


This is not the case. A good example would be Weav3r's site which has the API purpose table right below where the user enters the API.


Yours is not even providing the table nor is the purpose clear and visible in the place where the user provides the API key. At first I thought it was ignorance but nah, with you guys is always trying to push the limits of any rule and see what you can get away with, right?

LegendaryKing11 [2804919]

Good, so they're (technically) breaking the rules.


Seriously, put your ToS in the same page the user gives you the API. If you can't do this, you're shady af but you probably know this already. 


Let's see what staff has to say. 

Funky0 [3921686]

This is a scam don't ever enter your public or private API! 

They use it to mug and hurt your friends/traders..

Cleansing-Flame [1636350]

Original post just in case this is deleted: 

 "We don't use their personal data, events, logs, etc. We use their API key with their consent as a public key to look at other player's bazaar sales, not their personal data."


The way this reads is: you are bypassing the rules about scraping multiple pages by using other users to do it for you. The same multi page scrapings people are being fedded for, my suggestion would be to probably discontinue the bots and just use your own eyes. 


Thats just me.