Skip to content
TORNLIFE More

[API Leak] Stealth Attacker Identity Exposed via API / Discord Bot

Started by Ezlira [4037017] on in Bugs & Issues.

5 replies · 89 views · thread synced · 3 days ago · View on torn.com
About this thread

Posts archived: 6 / 6 posts (100%) · the total is Torn's reply count + the opening post at the last fetch

Counted by TornLife from the archived posts.

Archived posts
6
Discussion span
→
People posting
4
Likes on archived posts
2
Posts by staff, officers and moderators
2
Authority score
57 / 100
Historical score
30 / 100
Story score
38 / 100
Engagement score
51 / 100
Ezlira [4037017]

Hi,


I have discovered a potential API leak/exploit regarding stealth attacks and data exposure.


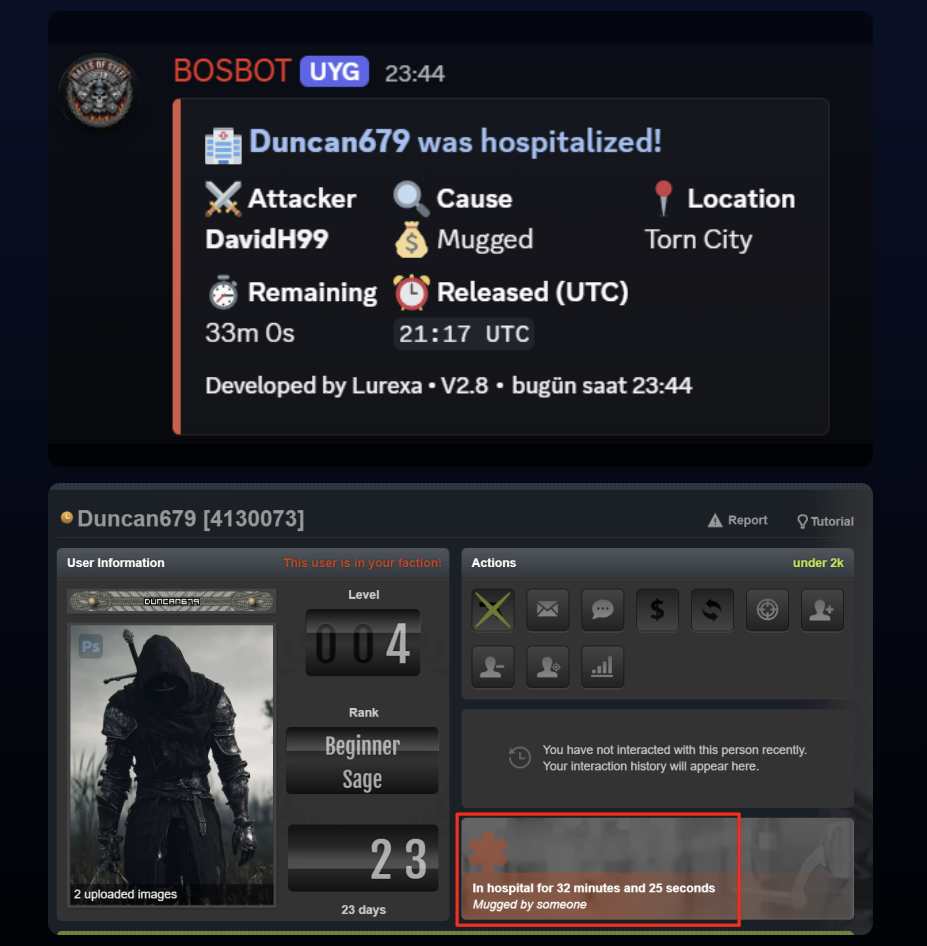
As you can see in the attached screenshots, when a player (Duncan679) is mugged with a successful stealth attack, the in-game UI correctly masks the attacker's identity, displaying "Mugged by someone".


However, our Discord bot, which pulls hospitalization/attack data from the Torn API, completely bypasses this stealth mechanic and explicitly reveals the attacker's real name (DavidH99) for the exact same event.


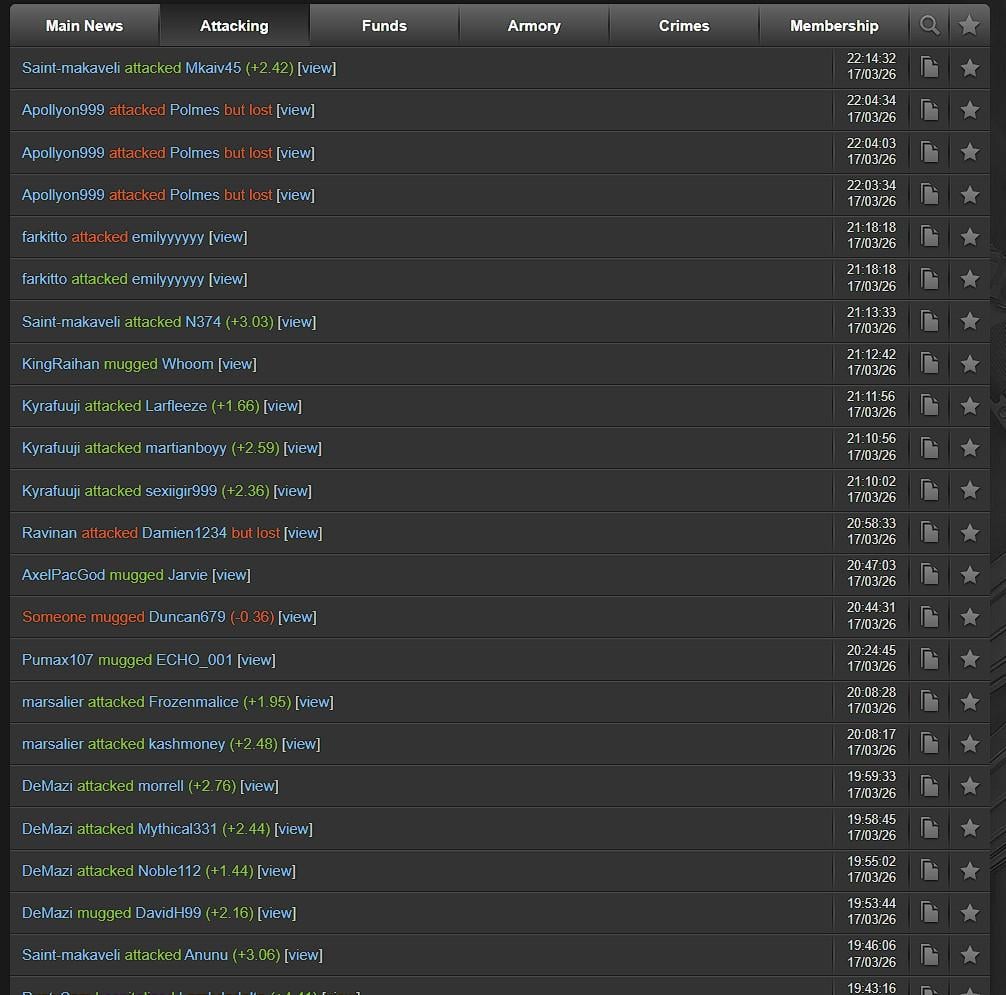
Furthermore, to rule out any coincidences, I also verified through the faction logs that the player was not mugged by anyone else during that specific timeframe. This confirms without a doubt that the bot and the in game UI are displaying the exact same attack.


The Issue: The API seems to be leaking the attacker's identity even when the attack was a successful stealth attack. This effectively renders the stealth mechanic useless, as anyone with a Discord bot or API access can easily see who attacked them.


Proof:

  • Image 1: Bot correctly parsing the API and showing the exact attacker (DavidH99).

  • Image 2: In-game profile showing the attacker is hidden as "someone".


Could you please look into why the API is exposing stealth attacker data? Let me know if you need more details or specific API logs.


ChatGPT [1762864]

I just checked and it appears to be working fine. Can you share the actual API response, as opposed to the output of your black box?


Can you also show the logs that Duncan679 was not mugged by someone else after being mugged by DavidH99?

CloudJumper [1636201]Staff

Are you sure your bot is working fine in the first place? This attacker has mugged this defender multiple times yesterday, some were stealthed and some were unstealthed hits. It is entirely possible that the bot is wrong and is showing you the name from the prior attacks which were unstealthed. Please provide the API response that is exposing the stealth, the devs won't be accessing your bot to figure out how you are displaying the data.

Ezlira [4037017]

Hi again,


I tried to retrieve the historical raw JSON for that specific attack, but I am unable to provide it for two reasons:

  1. Our bot processes the API data in real-time and we strictly do not store or keep logs of raw JSON payloads to save storage and respect privacy.

  2. I attempted to manually fetch the past attack log via the /user/4130073?selections=attacks endpoint using my API key, but I received an HTTP 403: Forbidden error (which is expected, as the API restricts viewing other players' attack histories retroactively).


However, the screenshot I provided in the original post is a direct output of what the API delivered to our bot at that exact timestamp. The bot simply maps the attacker_name and attacker_id fields. If the attack was properly stealthed at the API level, those fields should have been empty or masked, but they clearly weren't.


Moving Forward: I have now added a temporary logging mechanism to our bot's code. The very next time a stealth mug happens within our scope, I will capture the exact raw JSON payload and share it here for your debugging process.

Please let me know if the current screenshots are enough for your team to investigate the /faction/ or /user/ endpoint logic, or if you prefer to wait for my next raw data catch.

mavri [2402357]

> I attempted to manually fetch the past attack log via the /user/4130073?selections=attacks endpoint using my API key, but I received an HTTP 403: Forbidden error (which is expected, as the API restricts viewing other players' attack histories retroactively).

Just use the faction/attacks endpoint or ask the user for their API key.


> HTTP 403: Forbidden

Also I can tell you that's not the case because the API does not return non-200 OP codes, please vibecode less :)

CloudJumper [1636201]Staff

Mauro has checked this and has confirmed that we are not leaking the attacker ID for stealth attack anywhere. If you are able to find a valid example, where the API response is shown, then please file a new report.


Thanks!