same happend to me today, right after I've attacked i got notifications from torn tools, one of them was message "push now", was confused for a moment, didn't take SS, then i went to check on pop up window and i saw this
and it changed back to mine after few secs... so i wasn't able to get more details... but i had full stack at that moment and i was in torn, and our chain was not active
API issue
Started by Defectus [2549859] on in Bugs & Issues.
Posts archived: 40 / 40 posts (100%) · the total is Torn's reply count + the opening post at the last fetch
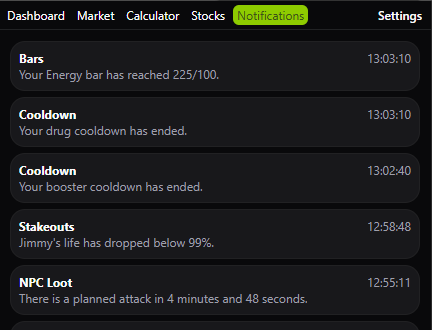
15:32TCT 19/06/2026
16:47TCT 19/06/2026
17:23TCT 19/06/2026
I received a torntools notification of a newsletter from a faction that I'm not in. I went to check my mail and it wasn't sent to me.
Also confirmed with the faction leader, that it was sent to the faction previously, with the information I was able to give back to them
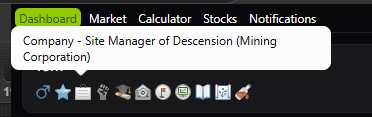
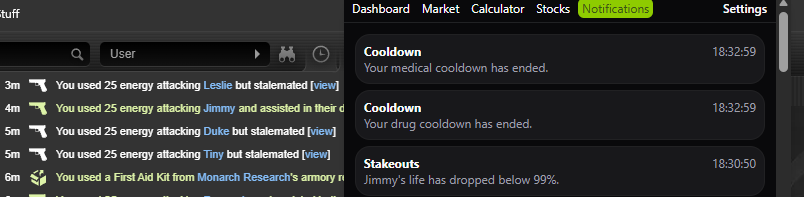
like expected its showing me other peoples data after each NPC fight
in this case its easy to point to daegum's Profile | Torn
Mentions: daegum [2679198]
This is also happening to me multiple times a day, sending me notifications my drug cooldown is over etc. when it isn't - when I check the dashboard I also get other peoples information.
18:44 TCT 19/06
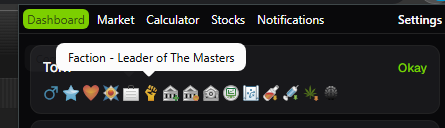

22:19TCT
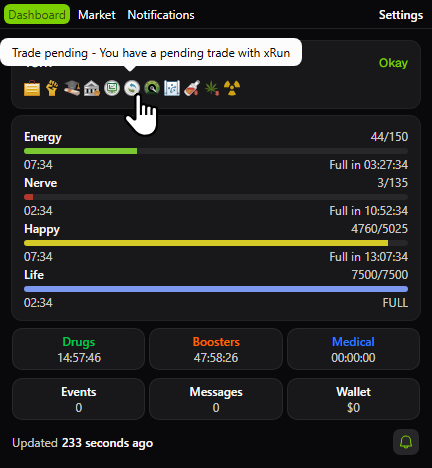
Yea received this notification not too long ago. Hopefully It is resolved soon as this is very concerning and compromising.
happend again, and notifications go like crazy when it happens...
Hey, im completely new to forums so kinda trying to figure out how to post stuff, but just wanted to say im having this issue too. Im collecting screenshot. I've seen a few here that are related to war notifications, and thats also what happened with mine. (it was a war push notification followed by energy 775/150) Both me and the faction leader i msg'd have contacted staff, and ill get some pics in here when i can (feeling sick with health stuff, as is normal for me)
I have also noticed weird flight notifications that dont match up with where im flying, but no statuses or bank/trade things like ive seen others post. will keep an eye out for that tho
Since devs cannot find anything on torn end probably safe to assume its something to do with TornTools, can the API access to this tool be blocked until fixed? I don't think people having access to bank times ending, money on hand, current trades etc its a good idea...
As the TornTools maintainer I will keep saying that it's not an error with TornTools itself. While I'll be keeping the exact details private, since I'm classifying this as a vulnerability somewhere on the Torn side and not just a regular bug/issue, I've likely found the situation that is causing this. I've let splent known privately what I believe the change on our end was that started triggering this.
Additionally I will be implementing something in TornTools where we'll start rejecting these compromising responses. That way our users won't receive that information on their screen or notifications. However, it's important to note that this is not an actual solution since the compromising responses will still be send and received, just no longer used. I've also decided against reverting the change or implementing another workaround where the responses will not be send either. Why? Because I'm afraid that it will then be marked resolved, even though the fundamental vulnerability would still be present and at some point likely appear again.
note: for those who don't know, splent is the API developer
Happened again immediately after attacking.
Hopefully Splent and DeKleineKobini have this in hand now as per the post above :)
Hey everyone,
This issue is now finally resolved. Big thanks to DeKleineKobini and other TornTools contributors as well as everyone who posted in this thread in helping us determine this is not TornTools specific issue, but a caching issue within Torn itself.
Some time ago, we enabled additional caching on ‘attacking’ related selections to help with enormous server load these selections sometimes go through.
However, this had also cached other selections alongside (by accident) if the API keys were sent as part of the ‘Authorization’ header.
This became highlighted only on June 13th, after TornTools switched from sending keys in the ‘Authorization’ header instead of as part of the query string. The sheer amount of requests from TornTools made this issue visible, but the bug itself has been around for a while, however, only for those requesting ‘attacking’ selections and using ‘Authorization’ headers.
This is also why this seemed to happen more frequently after players participated in attacking.
The Cloudflare caching is now fully disabled on api again so this should not happen again, and we learned to be much more careful with caching in the future.
Thanks.