Skip to content
TORNLIFE More

Yikes

Started by Jabajaba [2499335] on in General Discussion.

156 replies · 8.3k views · thread synced · 4 days ago · View on torn.com
About this thread

Posts archived: 157 / 157 posts (100%) · the total is Torn's reply count + the opening post at the last fetch

Counted by TornLife from the archived posts.

Archived posts
157
Discussion span
→
Authority score
62 / 100
Historical score
52 / 100
Story score
71 / 100
Engagement score
88 / 100

People posting, likes and official posts are not counted for this thread yet: on threads longer than one page they come from a periodic pass over the archive, which has not covered it.

Most-liked replies

Mentioned in this thread

Fr00t [2518990] ×1

Jabajaba [2499335]
Edit - TL;DR - reset API if you got it. Thanks all. Great job admin team.

Did anyone else just get this?

There is a concern that a third party application where you provided your API key may have exposed your key. As a precautionary measure, we recommend resetting your API key in your settings. No personal information relating to your Torn account is at risk.
Varides [2176530]
Yeah I just got it as well. What extensions do you use? I use, Torntools, Torn Data, and Tamper Monkey. Scripts currently used with Tampermonkey are Pennywise, Aquatools, and ID Chain watcher.

Maybe we can narrow it down.
__-___-___-__ [1921241]
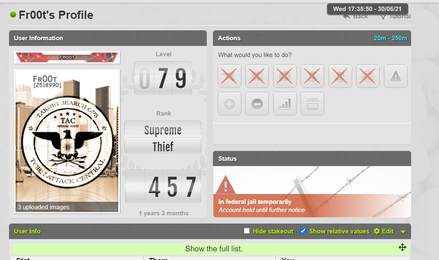
fr00t, committee member and person behind Torn Attack Central (TAC), is in fed. I've started the long journey of resetting my key and it's a PITA

17:16:56 - 30/06/21 You reset your API key

Plays into my concerns even for sites like TornStats, extensions like TornTools, etc. A more robust API Key system really is needed, and there is a ton of prior art on how to do it correctly. 1 API key shared amongst all tools, with no ability to limit which pieces of data is viewed, is basically the worst of all the available options.

Mentions: Fr00t [2518990] · Tornattackcentral - find targets for chains/mugs!

bogie [148747] Admin Staff
Hello all.

Unfortunately we received indication that TAC (Tornattackcentral) had a vulnerability resulting in the potential for API keys to be exposed. Whilst we do not believe there was any serious leak here this is a precautionary measure we have taken to ensure users are made aware.

If you received an event it means that your key had the potential to be exposed, if not then there was no risk - however if you feel unsafe please do reset your key.

I am in the process of speaking with Fr00t about this currently as there were some other concerns that needed to be raised with him regarding this site and their own personal activity that I cannot disclose at this time, however this has no major impact on anyone else at this time.

I have also spoken with Manuito since TornPDA utilizes features from TAC - However there is no risk to anyone who just uses TornPDA on its own, no data was shared from PDA to TAC, only information given directly to TAC is the concern at this time.

Rest assured no personal information related to Torn is at risk.


This is an excellent time to highlight that these third party sites and scripts can come with risk, and to give your API key out only to areas you can trust - Unfortunately however issues like this can and will come up from time to time - Creators are however required to comply with a certain level of security to keep information given to them on faith secure as detailed in the API documentation.

The API exists as a feature to ensure there is no risk of losing your secure and important Torn data, but do bear in mind it can carry a lot of information about your gameplay - it is sensible to limit how much you give this out.

Thank you everyone.
Varides [2176530]
Same here. I still had the old API key with limited access and this was exactly one of the concerns I had with updating to a new API key for full access
nex [2054500]
Who woulda thunk exposing too much info through the API would ever create a problem?

Totally unexpected. Nobody could've foreseen this.
Untouchable [1360035] Committee Committee
One key for all available account information including activity log to an app that only needs one specific thing?

Seems fine to me, move along.
Hamr [2027992]
Out of that list I'm using TornTools and Tampermonkey, and got the notif about API

My API is also at TornStats iirc
bogie [148747] Admin Staff
I don't think it's fair to say there's an issue with the API in this manner, this wasn't a fault of the API or with Torn's systems - they are and were working exactly as intended - this is an issue of insufficient security on a third party site, and fortunately because it was only API information the effect is very limited - even if what you were asking for in this scenario was in place it wouldn't really change anything - we would still recommend resetting the key - and the effect of what's exposed would be exactly the same given the purpose of TAC. However that's not my place to say whether or not such things can be added to Torn - perhaps this subject will highlight a necessary discussion for such things.